VX-1 IP Encryptor · Security hardware
A hardware network encryptor that protects every packet in FPGA silicon
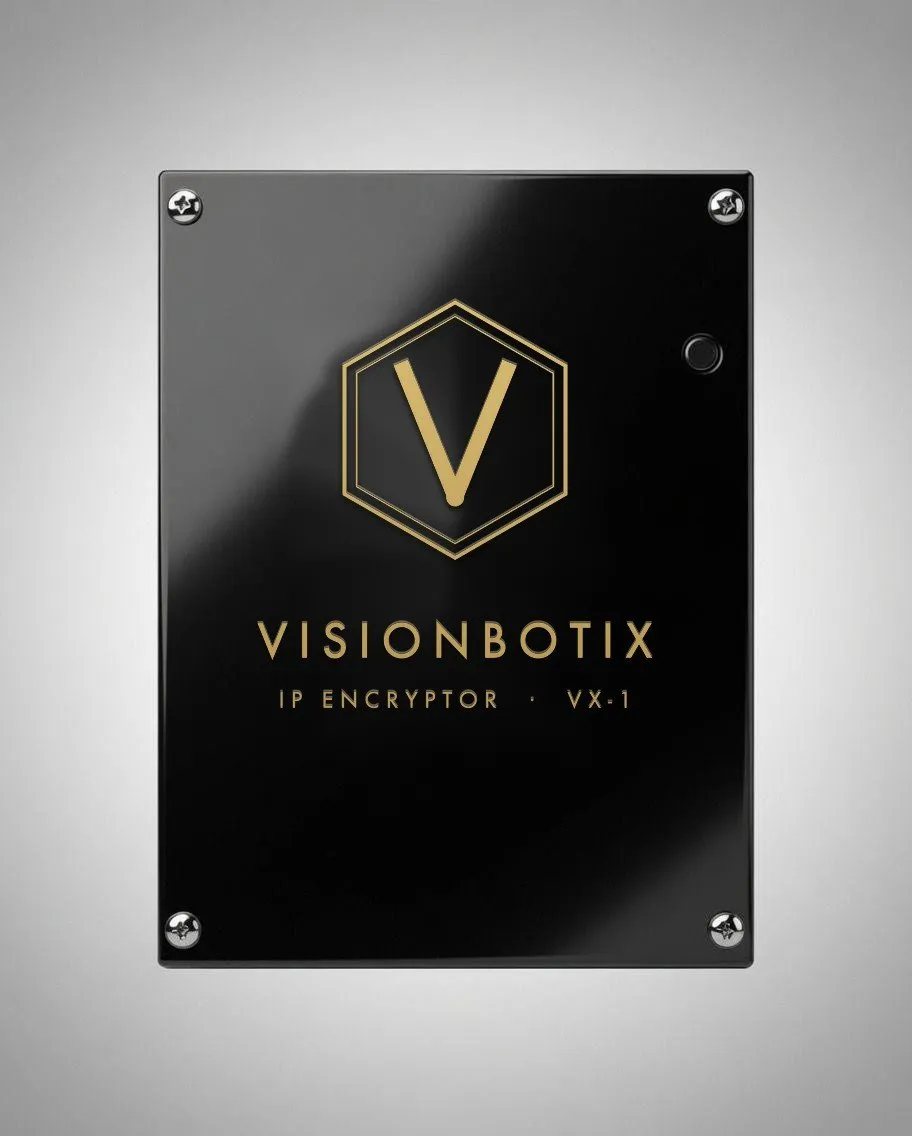
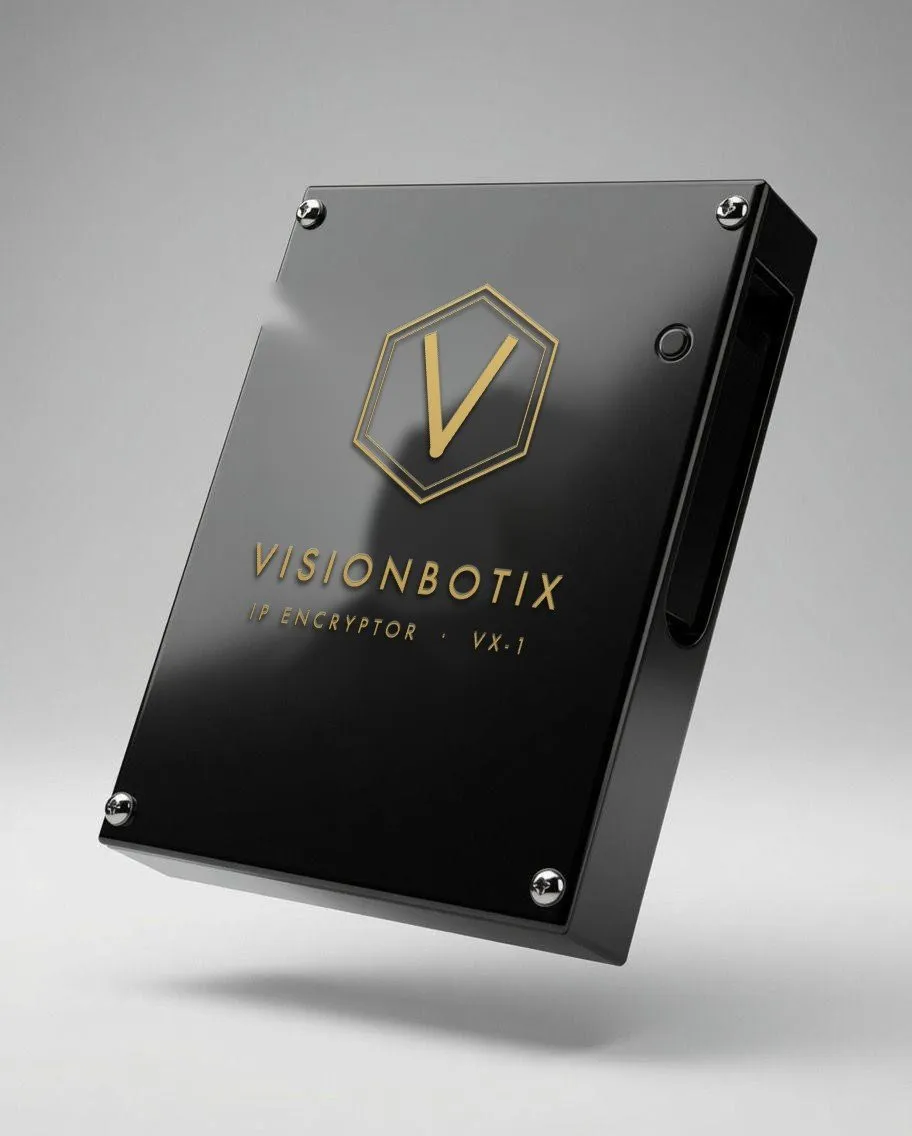
The VX-1 IP Encryptor is a hardware network encryptor from Visionbotix. It encrypts all IP traffic crossing your WAN with AES-256 in counter mode on dedicated FPGA silicon, with no operating system to attack. Place one unit at each end of a link and power on: it works transparently on Layer 2 and Layer 3 networks, including satellite links.
- AES-256 in counter mode, implemented fully in FPGA hardware
- No operating system, no background services, no software stack
- Plug-and-play on Layer 2 and Layer 3 links, including satellite
- Near line-rate throughput with low latency
Why it exists
The problem it solves.
Software encryptors and VPN gateways inherit every weakness of the operating system beneath them.
Each OS layer, background service and dependency adds patches, updates and configuration drift to manage.
Encrypting links usually means reconfiguring routers, switches and endpoints across every site.
Software encryption becomes a bottleneck when traffic peaks, so teams are tempted to switch it off.
What it does
Inside VX-1 IP Encryptor.
Encryption in silicon
AES-256 in counter (CTR) mode runs entirely on a dedicated FPGA, so every packet is encrypted in hardware.
Minimal attack surface
No operating system, background services or software dependencies, which removes most of the exposure malware relies on.
Zero configuration
Place one unit at each end of the link, connect and power on. No changes to routers, switches or endpoints.
Works over any WAN
Runs transparently on Layer 2 and Layer 3 networks, over ISP links, private WANs and satellite connections.
Line-rate performance
Hardware-speed encryption with near line-rate throughput, low latency and real-time packet processing.
Tamper and side-channel hardening
Built-in protections against side-channel attacks and hardware exploitation, with enhanced tamper resistance.
Tested in realistic conditions
Validated with multi-vendor routing and switching in the path and with real web, DNS, FTP, SMTP, VoIP and video traffic.
How it is deployed
From first briefing to running in your network.
Scope the links
A technical briefing on the sites, links and traffic you need to protect, under NDA on request.
Place a unit at each end
One VX-1 sits at each end of the WAN link, inline with your existing network equipment.
Connect and power on
There is no setup procedure. Your routers, switches and endpoints keep their current configuration.
Traffic is encrypted
All user data crossing the WAN is encrypted with AES-256 in hardware, with no software to patch.
Specifications
Technical overview.
- Encryption
- AES-256 in counter (CTR) mode, implemented fully in FPGA hardware
- Platform
- Dedicated FPGA with no operating system, no background services and no software stack
- Network layers
- Layer 2 and Layer 3, transparent to existing routers, switches and endpoints
- Supported links
- ISP links, private WANs and satellite connections
- Deployment
- Zero-configuration, plug-and-play, one unit at each end of the link
- Performance
- Near line-rate throughput with low latency and real-time packet processing
- IV handling
- Dynamic initialization vector (IV) generation
- Hardening
- Side-channel protections and enhanced tamper resistance
- Cryptographic check
- Ciphertext checked byte for byte against the NIST FIPS 197 reference vectors
- Performance testing
- RFC 2544 and ITU-T Y.1564 test suites, plus replayed real-world PCAP traffic, across VLAN, hybrid and enterprise topologies
Built for
Technical briefings, datasheets and pricing are shared under NDA. Availability may be subject to export-control rules.
Use cases
Where it earns its place.
Defense and government links
Secure communications between headquarters, field offices and remote sites over any transport.
Financial institutions
Encrypted transactions and inter-branch data flows without slowing the network.
Critical infrastructure
Protected links for industrial control systems, utilities and SCADA networks.
Telecom and ISP backbones
Encryption of backbone communications without reconfiguring carrier equipment.
Data center interconnects
Secure interconnects between data centers and enterprise sites.
Satellite and remote sites
Encryption for satellite links that serve remote or temporary locations.
See VX-1 IP Encryptor in a technical briefing.
Tell us about the links you need to protect. We will walk you through the VX-1 and discuss an evaluation deployment for your network.
NDA on request from the first call · You own 100% of the code and IP
Hardware encryptor vs software VPN
| Compared on | Software VPN or encryptor | VX-1 hardware encryptor |
|---|---|---|
| Where encryption runs | On a general-purpose operating system | On dedicated FPGA silicon |
| Attack surface | Full OS, services and software stack | No operating system, minimal surface |
| Deployment | Configuration on routers, gateways or endpoints | Plug-and-play, one unit at each end |
| Performance under load | Software bottlenecks as traffic grows | Near line-rate throughput, low latency |
| Maintenance | Patching, updates and configuration drift | No software to patch |
| Cipher | Varies by product and configuration | AES-256 in counter mode |
FAQ
VX-1 IP Encryptor: common questions.
What is the VX-1 IP Encryptor?
It is a hardware network encryptor built by Visionbotix on dedicated FPGA silicon. It encrypts all IP traffic crossing a WAN with AES-256 in counter mode at near line-rate speed, deploys plug-and-play with zero configuration and has no operating system, which keeps its attack surface minimal.
How is the VX-1 deployed?
You place one unit at each end of the link, connect it and power it on. It operates transparently at the IP layer, so your routers, switches and endpoints keep their current configuration.
What networks does the VX-1 work on?
It works on Layer 2 and Layer 3 networks, including ISP links, private WANs and satellite connections. It has been tested with multi-vendor routing and switching equipment in the path, across VLAN, hybrid and enterprise topologies.
Does the VX-1 run software that needs patching?
No. It has no operating system, no background services and no software stack. Encryption runs entirely in FPGA hardware, which removes the patching, updates and configuration drift that software encryptors need.
How is the VX-1 different from a software VPN?
A software VPN runs on an operating system that needs patching and can be attacked. The VX-1 encrypts in FPGA hardware with no operating system, needs no configuration and keeps near line-rate throughput with low latency.
How was the encryption validated?
The AES-256 output was checked byte for byte against the NIST FIPS 197 reference vectors. Performance was measured with the RFC 2544 and ITU-T Y.1564 test suites, and real web, DNS, FTP, SMTP, VoIP and video traffic was verified to pass uninterrupted.
How much does the VX-1 cost?
The VX-1 is quoted per deployment, based on the number of links and sites. Ask for a technical briefing and we will prepare a quote for your network.
Something else? info@visionbotix.com or send us a message.Updated 19 November 2026
More of our products
Also built in-house.
Wakeel
AI lawyer matching for Pakistan, in Urdu, English or Roman Urdu.
ThreatIQ
Internal defense layer for air-gapped networks.
Cyber Range
Red/blue team training and device testing.
Ready to put AI to work?
Book a free 30-minute strategy call. We map where agents save you the most time, and you leave with a plan whether or not we work together.
NDA on request from the first call · You own 100% of the code and IP